ERP Security: Protecting the System That Knows Everything
- Sep 23, 2026
- Isha Taneja
ERP systems hold every critical piece of business data an organization owns. Here is why ERP security has become the most urgent cybersecurity priority of 2026.
ERP systems hold every critical piece of business data an organization owns. Here is why ERP security has become the most urgent cybersecurity priority of 2026.
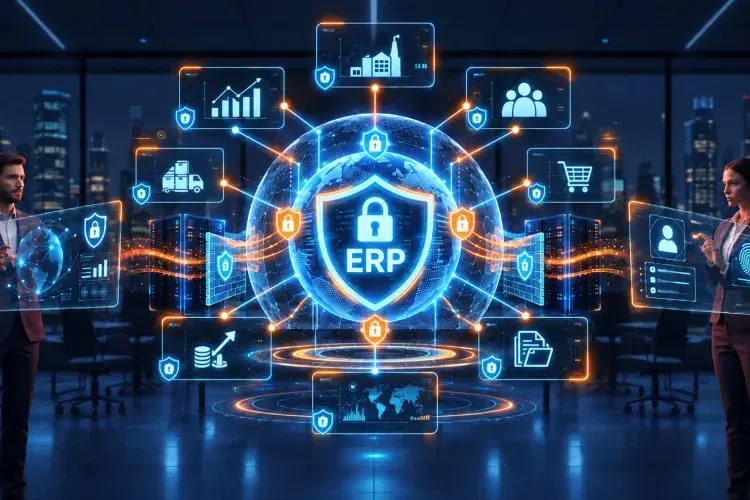
Enterprise resource planning systems hold more sensitive business data than any other system in the organization. Financial records. Employee data. Customer information. Supplier contracts. Pricing structures. Inventory levels. Compliance documentation. Intellectual property embedded in production workflows.
When a business application is breached, it exposes the data that a specific application manages. When an ERP is breached, it exposes everything the organization knows about how it operates, who it serves, what it earns, and how it competes.
IBM's 2025 Cost of a Data Breach Report put the global average cost of a data breach at $4.4 million. For breaches involving enterprise resource planning systems specifically, the cost is higher because the scope of exposed data is broader, the recovery complexity is greater, and the regulatory exposure spans every compliance framework the organization operates under simultaneously.
This is the security conversation most organizations are not having at the right level. ERP security is not an IT department responsibility. It is a board level business risk that belongs in the same conversation as financial controls, legal exposure, and reputational protection.
ERP systems are the single most data rich environment in most organizations. A breach exposes financial, operational, employee, customer, and supplier data simultaneously making ERP the highest value target for any attacker with access to the network.
Access control. Organizations routinely grant broader ERP access than individual roles require, creating large internal attack surfaces where a single compromised credential exposes significantly more data than necessary.
It depends entirely on implementation. Cloud ERP deployed correctly through a major vendor with mature security architecture typically delivers stronger security than on-premises ERP maintained by an internal team. Cloud ERP deployed without proper access controls, data classification, and monitoring creates a security environment that is simultaneously more accessible and less governable than the on-premises system it replaced.
The global ERP software market reached $106.22 billion in 2026, up from $92.6 billion in 2025. Cloud deployments now account for more than 70 percent of all ERP implementations. The combination of an enormous and growing market and an accelerating shift to cloud-based access has expanded the ERP attack surface faster than most organizations have expanded their security posture to match it.
The threat is not theoretical. ERP systems have been the specific target of sophisticated attack campaigns because attackers understand exactly what they contain. Financial fraud through ERP access can be executed quietly over extended periods before detection. Intellectual property theft through ERP access can expose years of competitive advantage. Ransomware targeting ERP data has a higher leverage effect than ransomware targeting any other single system because operations across every business function halt simultaneously.
ERP software is particularly favored by manufacturing companies at 21 percent of deployments, followed by banking and financial services at 16 percent, and telecoms at 13 percent. Each of these industries has specific regulatory frameworks, covering financial reporting accuracy, data privacy, and operational integrity, where an ERP security breach produces compliance violations alongside the operational disruption. The cost of a breach in these environments includes regulatory fines, remediation costs, and the reputational damage of disclosing a breach to regulators and customers simultaneously.
Understanding where ERP security breaks down is more useful than a general list of security recommendations. Four failure patterns appear consistently across industries and deployment models.
Excessive access rights accumulated over time. ERP access rights are granted when employees join, change roles, or take on temporary responsibilities. They are rarely revoked with the same discipline. Over years of normal business operation, the average ERP environment accumulates extensive access rights that are no longer aligned with actual job functions. An employee in their fifth role within the organization typically retains the access granted in their first, second, third, and fourth roles alongside the access their current role requires. This accumulated excess creates an internal attack surface that a single phishing success or compromised credential can exploit at significant scale.
Customizations that bypass security controls. ERP customizations written to support specific business processes frequently bypass the security architecture of the core platform. A custom report that accesses data across modules to serve a legitimate business need may have been written without the access controls that govern the same data in the standard platform. These customizations accumulate over years and create undocumented access paths that standard security audits frequently miss.
Inadequate monitoring of privileged accounts. ERP administrator accounts have unrestricted access to every module and every dataset in the system. The activity of these accounts is frequently logged but rarely monitored in real time. A compromised administrator account can operate undetected for extended periods long enough to extract significant data or establish persistent access before the compromise is identified.
Integration points that inherit excessive permissions. Modern ERP environments are connected to dozens of other systems through APIs, middleware, and data exchange processes. Each of these integration points represents a potential entry into the ERP environment. Integration accounts are frequently granted broad ERP access to avoid errors rather than the minimum access required for the integration to function. Every integration account with excess permissions is an unguarded entry point.
The move to cloud enterprise resource planning has changed the infrastructure security model significantly. It has not changed the access control, data governance, and monitoring requirements that determine whether an ERP environment is secure.
Cloud ERP vendors operating at scale: Oracle, SAP, Microsoft, Workday invest in infrastructure security at a level most individual organizations cannot match. Physical security, network security, infrastructure patching, and availability protection are handled by teams whose sole focus is the security of that platform. For organizations previously managing premises ERP on aging infrastructure with limited security staff, cloud ERP represents a genuine security improvement at the infrastructure layer.
What cloud ERP does not automatically provide is application security. Access controls, user provisioning, data classification, audit trail configuration, and monitoring are still the responsibility of the organization implementing and managing the system. The cloud vendor secures the platform. The organization is responsible for how that platform is configured, who has access to it, and what happens when that access is compromised.
SaaS ERP solutions are growing at 17.4 percent annually, outpacing traditional on premises deployments. That growth rate means that a significant number of organizations are moving to cloud ERP without having fully resolved the access management, data governance, and monitoring questions that determine whether the cloud ERP environment is more or less secure than what it replaced.
One of the most significant security trends in ERP for 2026 is the integration of blockchain technology as a security and audit layer for specific ERP functions.
Industry leaders including SAP and Microsoft are already integrating blockchain into their ERP platforms to enhance security and transparency in business operations. The value proposition is specific. Blockchain's decentralized and tamper proof design makes transaction records fraud proof and error free in a way that conventional database audit logs cannot match because conventional logs can be altered by anyone with sufficient system access, while blockchain records cannot be retroactively modified.
For supply chain transactions, financial settlements, and compliance documentation the categories of ERP data most frequently targeted for fraudulent modification blockchain provides an audit trail that is independently verifiable and immutable.
Organizations in industries with strict compliance requirements including healthcare, finance, and manufacturing are exploring blockchain within ERP specifically to meet audit and reporting standards more effectively.
Blockchain ERP integration is not yet mainstream but is advancing fast enough that organizations making ERP vendor selections in 2026 should include the vendor's blockchain roadmap in their evaluation criteria alongside AI capability and cloud architecture.
Five practices separate organizations with genuinely secure ERP environments from those that believe their ERP is secure because it has not yet been breached.
| Practice | Description |
|---|---|
| Conduct a regular access rights audit | Map every user's current ERP access against their current job function. Revoke access that is no longer required. Implement a process that removes access automatically when an employee changes roles or leaves the organization rather than relying on manual revocation that is frequently incomplete. |
| Implement role-based access at the module and field level | Access rights should be defined by role, not by individual. A financial analyst should have access to the financial modules their role requires and no others. A procurement manager should have access to procurement data and supplier records without access to employee compensation data. Defining access at this level of granularity reduces the damage any single compromised credential can cause. |
| Monitor privileged account activity continuously | Administrator and superuser accounts should be subject to real time activity monitoring with automated alerts for unusual behavior patterns access at unusual hours, access to data categories not previously accessed, bulk data export activity. The monitoring that most organizations apply to privileged ERP accounts is log based and reviewed periodically. It needs to be real time to be meaningful. |
| Review and secure all integration points | Document every system connected to the ERP. For each integration, confirm that the integration account has the minimum access required for the integration to function. Remove excess permissions. Monitor integration account activity with the same rigor applied to human user accounts. |
| Test security controls regularly against realistic attack scenarios | Security controls that have not been tested have not been validated. Regular penetration testing that specifically targets the ERP environment including its integration points, its customizations, and its privileged accounts provides the evidence that controls are functioning as designed rather than the assumption that they are. |
Build the data governance and security foundation your ERP environment actually requires. Talk to Complere Infosystem today.


Listen in for business strategies and interviews with business experts to help you build a business and a life that you love.
About Us